Tufin.club
  • www.tufin.club
  • imprint
  • data privacy statement

www.tufin.club

Tufin Orchestration Suite 5.4.00

Details
Version update
Last Updated: 26 October 2026

Tufin has officially released TOS 5.4.00. It's available as GA and can be downloaded from the Tufin Portal (authentication and subscription contract required).
Some improvements of TOS 5.4.00:

  • SecureTrack:
    • Updates in TQL - GraphQL
      In Rule Viewer and GraphQL API rules can be filtered by device status - enabled or disabled - to focus on active devices. This eliminates the need to manually exclude inactive device rules from policy analysis. Additionally, device status is exposed as a field in the GraphQL API rule projection.
    • The search in Rule Viewer is improved; now rules can be searched for USP violation count.
    • When navigating away from rule viewer, no the last TQL query and results are automatically restored when returned to the view within the same session.
    • Segmentation Intelligence analysis can now be configured directly from a dedicated settings page. Configurable items, including reporting mode, subnet volume limits, and zone, model, and device exclusions, are now accessible without requiring back-end intervention, and apply to the next analysis run.
    • When managing networks with overlapping IP address spaces, now the source domain in Path Analysis can be specified. This ensures that the correct network is targeted. A new optional Source Domain field appears in the Topology Map when overlapping IP mode is enabled and the default domain view is active.
  • SecureApp 
    • It's now possible to revert changes made to a SecureApp application connection (add/edit) since the last ticket was created (via API only). 

  • Vendor specific  
    • Akamai Guardicore
      • It's supported now to enforce the Unified Security Policy against tag-based assets residing inside rules. Additionally, USP security zones that include tag strings can calculate violations by matching zone tags against object tags and tagged assets in security rules.
      • SecureTrack now accurately reflects in Path Analysis the real-world enforcement, delivering reliable information about traffic being allowed or blocked. Each microsegmentation asset in the path now shows its enforcement mode (Visibility-only, Monitoring, Selective Enforcement, or Full Enforcement), the resulting allow/block decision, and the specific rule that drove it.
    • Amazon Web Services (AWS)
      • For AWS Network Firewalls now unused rules are identified. So optimization recommendations can be provided by TOS. Last hit data and rule optimizer support have been extended to AWS Network Firewall, and last hit data for these rules is shown in Rule Viewer.
      • Also for AWS Network Firewalls TOS provides now policy visibility and topology support. It includes AWS Firewall Policies, their rulesets, and associated firewalls. Therefore, rules can be searched in Rule Viewer, USP violations are recognized as well as checking the packets passing the topology. 
      • AWS resources are enhanced. The license usage report now counts any resource type attached to SGs beyond VMs, including NLBs, ALBs, VPC Endpoints, etc. as part of the CLOUD-VM type. Prefix lists are now supported as part of the SG rules in TOS, making license usage more transparent.
    • Broadcom
      • For Broadcom VMware, migrating to VMware Cloud Foundation (VCF) with NSX 9.1 can now use TOS without losing any functionality.
      • When having Broadcom NSX, the modify group workflow now supports IPv6, improving the automation abilities. 
    • Check Point
      • IPv6 for Check Point is now supported by the "modify group workflow". Dual Stack network objects are supported - therefore these objects as well as IPv4 and IPv6 are supported by this workflow.
    • Fortinet
      • FortiGate managed through FortiManager Cloud don't need on-prem FMG appliances. Additionally, TOS supports the cloud-based FortiCloud authentication.
      • When using FortiManager with global-only object policies, network changes can now be automated. SecureChange provisions new objects directly as global objects in FortiManager, and leverages existing global objects as part of the change process. Additionally, SecureChange provisions services and object groups as global objects, and synchronizes them from the Global ADOM to the assigned Local ADOMs.
      • When renaming a FortiManager VDOM, there is no more a need to re-import FortiManager firewalls and VDOMs after having devices renamed or moved between ADOMs. 
    • Illumio
      • FSecureTrack now accurately reflects in Path Analysis the real-world enforcement, delivering reliable information about traffic being allowed or blocked. Each microsegmentation asset in the path now shows its enforcement mode (Visibility-only, Monitoring, Selective Enforcement, or Full Enforcement), the resulting allow/block decision, and the specific rule that drove it.
    • Palo Alto Networks
      • Strata Cloud Manager (SCM) TOS now supports dynamic and static route resolution in topology, including IPv6. This routing information is retrieved directly from the local gateway firewalls.
      • Palo Alto App ID is supported now in blocking policies within the Unified Security Policy.
      • Having Palo Alto security policies, they can be improved by the use of USP violations. To do so, the USP cell property can be configured to raise a violation when a Security Profile Group or Log Forwarding Profile is missing on NGFW rules.
      • Predefined DNS Application Recognition in Topology Map are supported and considered now.
      • For Panorama, it can be exactly seen which devices a Panorama rule targets, with accurate shadowing analysis and topology calculations that take the Target field into account. This Target field is supported in Rule Viewer as well as Compare Revision, Shadowing and Topology Path Simulation.
    • Stormshield
      • SNS firewalls are supported now, with full policy visibility, USP compliance, change tracking, topology, and SecureChange automation. Native OPM integration connects directly to each SNS firewall. 

Further improvements, as well as corrections, are included in TOS 5.4.00.
The latest version of the Tufin Orchestration Suite can be found and downloaded from the Tufin Portal: https://portal.tufin.com


Vulnerabilities in PHP

Details
Basics
Last Updated: 22 October 2026

Two serious vulnerabilities in PHP have been found and published. Several web servers were taken down until they have been patched. 

As Tufin points out in their knowledge base, TOS and TufinOS are not affected by CVE-2026-109618 or CVE-2026-109619.

So, no action is required, and there's no patch or mitigation to apply.


Tufin Orchestration Suite 5.3.00

Details
Version update
Last Updated: 20 August 2026

Tufin has officially released TOS 5.3.00. It's available as GA and can be downloaded from the Tufin Portal (authentication and subscription contract required).
Some improvements of TOS 5.3.00:

  • Amazon AWS Network Firewalls are supported now in SecureTrack regarding Policies, Rule Bases as well associated Firewalls.
  • AWS Cloud WAN is supported to retrieve and model Network Function Groups (NFGs) and their service insertion configuration in the Topology Map.
  • Regarding any AWS Resource Type (generic resources) are supported by SecureTrack, i.e. support of NLBs, ALBs, private/public VPC endpoints, and more, in addition to EC2 instances, representing them as network entities in the revision, topology map, and path analysis.

  • Cisco L3 switches now can be imported to SecureTrack via Bulk Device API, as it has been possible before for routers and other L3 devices.
  • For Cisco Meraki provisioning of changes is possible for Meraki MX devices, as it is for other platforms before. Site-to-Site VPN rules are placed at the organization level, Layer 3 firewall rules at the per-network level, and group policy rules at the per-group-policy level. 

  • For Check Point, SecureTrack supports Object Usage (last hit), Rule Viewer now also displays the statistics for FQDN/domain-based objects.

  • Microsoft Entra ID is supported now as it is Active Directory (AD) on prem. Entra ID user groups can be used for topology and end-to-end access requests.
    Currently supported for Palo Alto Panorama and Strata Cloud Manager only.

  • Palo Alto Networks (PAN) Strata Cloud Manager is supporting dynamic as well as static routes in the Topology Map. 
  • Strato Cloud Manager allows automation for Strata Cloud Manager (SCM) NGFW Folders in Access Request Workflows for IPs when in Topology Mode. Support of Designer, Verifier, and Provisioning.
  • PAN Shared Gateways with shared gateway interfaces are supported by the Topology Map now. They are mapped to their privacy zones as defined in the PAN devices.
  • For Palo Alto Panorama-managed Firewalls information about "rule last hit" can be retrieved via API now. 

  • NSX devices are supported better regarding rule matching. It now now considers traffic associated with Security Groups (SGs) specified in the NSX rule's Applied To field,
  • NSX-T Distributed Firewalls (DFW) are supported in SecureChange Access Requests without activated Topology (Designer, Verifier, Provisioning).
  • NSX Security Group (SG) types are fully supported now across Rule Viewer as well as Topology Map.
  • Syslogs following RFC-5424 are supported for NSX devices now. '

  • SecureTrack shows additional new options 
    • Zones and Subnet Data are analyzed in regard of configuration errors, hints are delivered
    • USP violations consider now User Identity also (no subnet specification), they are validated agains a pre-defined User Network Zone. 
    • SecureTrack Rule Viewer has a new TQL field: "added", so rules can be searched for the date they were added
    • SecureTrack Rule Viewer supports the search for 3rd party vendors (OPM) now.
    • SecureTrack Rule Viewer allows to search for rules regarding Security Zones containing source or destination IP

Further improvements, as well as corrections, are included in TOS 5.3.00.
The latest version of the Tufin Orchestration Suite can be found and downloaded from the Tufin Portal: https://portal.tufin.com


Tufin Orchestration Suite 5.x

Details
Version update
Last Updated: 07 July 2026

After referencing the publication year in the version since 2012, Tufin now has introduced the new naming convention - starting with 5.0.00 (even if that version number has already been published in 2010/2011).

Starting with 5.0.00 Tufin will provide major versions (PGA) and hotfixes (PHF), respectively. Regarding versions this needs to be considered

  • Platform version, e.g. TOS 5, TOS 6
  • Initial release version, e.g. 5.0.00, 6.0.00 -> not for production
  • Feature version, e.g. 5.1.0, 5.2.0 with feature enhancements, bug fixes, but hardly any infrastructure changes

In version 5.1.0 some new features and options have been integrated

  • Operating System:
    TOS can now be installed on Red Hat Enterprise Linux 9 and Rocky Linux 9 operating systems

  • For Amazon AWS, TOS now supports not only SDKv1, but also SDKv2 for AWS Monitoring. SDKv1 has reached End of Support.
  • Amazon AWS RDS instances are now visible in TOS. It requires AWS SDKv2 and delivers some advantages (details here).   
  • Amazon AWS accounts can be monitored by TOS, i.e. AWS opt-in regions using assume role authorization. SDKv2 required.
  • Arista VeloCloud SD-WAN devices can now be monitored by TOS
    Please follow these links to find information about feature support in SecureTrack and SecureChange.
  • Cisco IOS-XE SDWAN (cEdge) - GRE Tunnel is supported by TOS now, more here.
  • Regarding Cisco FMC, FQDN objects are supported now in SecureTrack and SecureChange.
  • In Microsoft Azure, TOS now supports VNet flow logs when configured correctly.

  • Tufin AI support is integrated, allowing e.g. own dashboards and reports.

TOS 5.1.0 is available in the Download Section of the Tufin Portal: https://portal.tufin.com (authentication required).


TufinOS 4.70 available

Details
Version update
Last Updated: 11 June 2026

In April, Tufin has released TufinOS 4.70, based on Rocky Linux 8.10 latest versions. 
It includes Kernel version 4.18.0-553.89.1.el8_10.x86_64 and 105 updated RPMs. TufinOS includes now 755 RPMs in total. 

TufinOS is available for Tufin Appliances Gen 4.0 (T-800, T-1200), as well as Gen 4.5 (T-820, T-1220) and the new Gen 5.0 applicances (T-900, T-1300). 
It cannot be deployed on Gen 3.5 appliances T-1100XL and T-1100 (!)
As before, the supported hypervisor is VMware. 

TufinOS is available in the Download Section of the Tufin Portal: https://portal.tufin.com (authentication required).


Granular SLAs for Workflows

Details
SecureChange
Last Updated: 11 June 2026

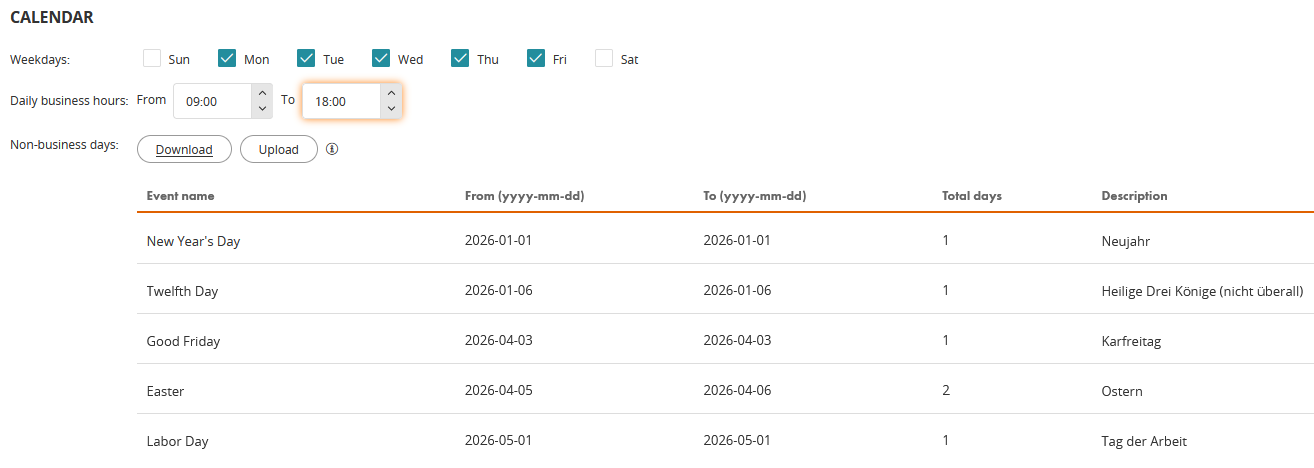
Since many years it's possible to configure SLAs for SecureChange Workflows. In earlier times, there was no option to disregard e.g. weekends. So if a step needed to be completed within 2 days, a problem was there during weekends: Step started on Friday afternoon and not worked on until Monday. 

Today, a granular configuration is possible. It's done in SecureChange via Menu > Settings > SecureChange > Miscellaneous. 

As shown above, it's possible to define business hours as well as business days. Additionally, there is an option to import / export further dates like e.g. public holidays. When exporting the list as CSV file, it should not be edited in Excel - the import will fail afterwards. It's recommended to modify this file with a simple editor like Notepad++ or similar. Then, the import is usually successful.
Please find below a sample for 2026 (Germany) that you can copy, modify and import into your TOS installation. 

"name","from_date_yyyy-mm-dd","to_date_yyyy-mm-dd","comment"
"New Year's Day","2026-01-01","2026-01-01","Neujahr"
"Twelfth Day","2026-01-06","2026-01-06","Heilige Drei Könige (nicht überall)"
"Good Friday","2026-04-03","2026-04-03","Karfreitag"
"Easter","2026-04-05","2026-04-06","Ostern"
"Labor Day","2026-05-01","2026-05-01","Tag der Arbeit"
"Ascension Day ","2026-05-14","2026-05-14","Christi Himmelfahrt"
"Pentecost","2026-05-25","2026-05-26","Pfingsten"
"Feast of Corpus Christi","2026-06-04","2026-06-04","Fronleichnam (nicht überall)"
"Feast of the Assumption","2026-08-15","2026-08-15","Mariä Himmelfahrt (nicht überall)"
"German Unity Day","2026-10-03","2026-10-03","Tag der deutschen Einheit"
"All Saints' Day","2026-11-01","2026-11-01","Allerheiligen (nicht überall)"
"Christmas","2024-12-24","2025-12-26","Weihnachten"
"New Year's Eve","2026-12-31","2026-12-31","Silvester"


Page 1 of 26
  • Start
  • Prev
  • 1
  • 2
  • 3
  • 4
  • 5
  • 6
  • 7
  • 8
  • 9
  • 10
  • Next
  • End
Bootstrap is a front-end framework of Twitter, Inc. Code licensed under MIT License. Font Awesome font licensed under SIL OFL 1.1.